IAM Engineer · Sarajevo · Remote

Identity infrastructure that is secure, auditable and run as code.

I'm Elvir, an identity and access management engineer. In my current role I operate a multi-realm Keycloak platform for a health-tech company — brokering hundreds of external SAML and OIDC federations alongside Microsoft Entra ID and LDAP / AD, with the configuration kept in Terraform and the repetitive work automated with Python and an AI agent.

Before that I spent two years in a security operations team. In 2026 I delivered a partner-authentication platform for a UK proptech as its sole Keycloak owner.

Taking on B2B contracts for teams in the UK, EU and US.

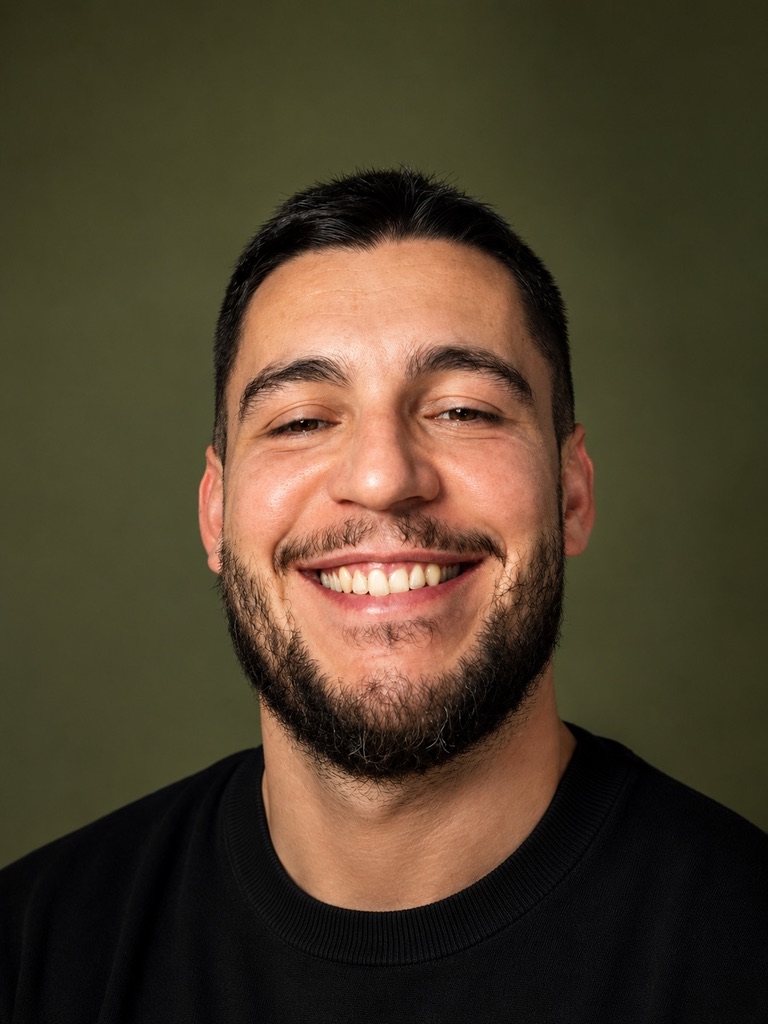
Portrait of Elvir Đedović
Sarajevo, Bosnia and Herzegovina · CET
4+ years in identity and security, since December 2021
Keycloak · Entra ID · AD operated in production environments
ISO 27001 · PCI DSS experience in environments aligned to both
Services

Where I can help.

For teams that run Keycloak or another identity platform and need it secure, federated and maintainable — without hiring a full-time IAM engineer.

01

Keycloak review & hardening

A structured review of realms, clients, mappers and authentication flows — token audience and issuer, TLS, brute-force settings, admin exposure — with a written report and prioritised fixes.

02

SSO & federation

Connect customer and partner identity providers over SAML 2.0 and OIDC, broker Microsoft Entra ID, federate LDAP / AD, and map claims so every application gets the identity it expects.

03

Identity as code

Realms, clients and mappers in Terraform / Terragrunt with per-environment state and CI — every identity change becomes a reviewed diff instead of a click in the admin console.

04

Migration to Keycloak

Move from Auth0, Okta, Cognito or a legacy provider in phases, using identity brokering and password-hash bridging, designed to avoid forced password resets.

05

Identity automation

Python tooling against the Keycloak Admin API for repetitive work — test users, client onboarding, bulk changes and configuration checks — plus AI-assisted automation that turns onboarding tickets into configuration changes for review.

06

Ongoing IAM support

A fixed number of hours each month for teams without an in-house identity owner: changes, upgrades, reviews and incident help during business hours.

Fixed scope, fixed price. Every engagement is agreed after a free 30-minute call.

Selected work

Recent identity projects.

Client and employer names are left out on purpose; details are available in conversation.

UK proptech Contract via Explore Group Apr – Jun 2026

Partner authentication, from greenfield to go-live

Context

The company needed its partners to sign in to a web app and call its API securely, with Keycloak as the identity provider and nothing built yet.

What I did

As the sole Keycloak owner I designed the partner realm: Authorisation Code + PKCE for the single-page app, client-credentials service accounts for partner API access, and audience-scoped access tokens enforced end to end. I built the configuration as code from scratch — reusable Terragrunt modules for local, UAT and production — so every realm, client and mapper change became a reviewed Terraform diff.

Result

I led the pre-go-live security review of the realm and remediated its findings before go-live.

  • Keycloak
  • OIDC
  • PKCE
  • Client credentials
  • Terragrunt
  • AWS
Health-tech platform Current role 2024 – present

One identity broker for many customer identity providers

Context

Customers sign in through their own identity providers — some SAML 2.0, some OIDC — while every product and internal service needs one consistent identity and the authorisation data that goes with it.

What I do

I operate a multi-realm Keycloak platform that federates those providers behind a single authentication layer, covering inbound and outbound SSO over SAML and OIDC. I onboard and troubleshoot integrations with Okta, PingIdentity, Microsoft Entra ID, Active Directory and custom-built customer identity providers, manage LDAP / AD federation including attribute mapping and conflict resolution, keep the SSO configuration in Terraform and automate routine SSO work in Python.

Also

A JWT customisation framework built on protocol mappers that puts organisation-specific claims and RBAC data into tokens, so downstream services can make fine-grained authorisation decisions without their own identity logic.

  • Keycloak
  • SAML 2.0
  • OIDC
  • Okta
  • PingIdentity
  • Entra ID
  • LDAP / AD
  • Terraform
  • Python
AI-assisted automation Health-tech platform Current role

An AI agent that turns SSO tickets into reviewed changes

Context

Every new customer SSO connection, removal and certificate rotation arrives as a ticket that an engineer would otherwise translate into configuration by hand.

What I built

An agent on AWS Bedrock that reads the ticket requirements, parses them and generates the configuration change as a merge request. The engineer only reviews and applies it, so a human always approves the change. It covers onboarding, offboarding and certificate rotation.

Also

Weekly automated checks review the SSO configurations, flag certificates that are about to expire and open tickets, so customers are warned before anything breaks.

  • AWS Bedrock
  • LLM agents
  • Terraform
  • Python
  • Human-in-the-loop
Security operations Health-tech company 2022 – 2024

Automatic account lockdown on suspicious activity

Context

In the security operations team, responding to suspicious account activity meant manual steps for the incident response team.

What I did

I built Python and Rapid7 automation that hard-locks accounts when suspicious-activity triggers fire, alongside administering Microsoft Entra ID — conditional access, MFA enforcement, identity governance and access reviews across Microsoft 365 and Azure.

Result

Less manual response work for the incident response team on account-compromise alerts.

  • Python
  • Rapid7
  • Entra ID
  • Conditional access
  • MFA
Recommendations

What people I've worked with say.

“Elvir joined us on a short-term contract to support work involving Keycloak and related identity/access management challenges. He was a very pleasant and professional person to work with, collaborated well with the team, and made a valuable contribution during his time with us.

He brought useful experience to an area where we needed additional capability, helped us make progress on important technical work, and was always constructive in how he engaged with feedback and discussion. I appreciated his support and wish him well in his future roles.”

Neil Reilly Head of Engineering / VP Engineering · Regulated SaaS Managed Elvir directly · July 2026

“Elvir is a valued member of our Offshore CyberSecurity analyst team. In addition to his positive attitude, he is a solid performer always willing to pitch in when needed in other areas. His desire to learn new things and ability to work with minimal supervision even halfway across the world would be a benefit to any company.”

Kris Kistler, MS, CISSP CISO, Access Telecare Senior colleague · June 2024

“He brings a unique blend of technical expertise and exceptional soft skills to the table. He excels in conducting security assessments, analyzing vulnerabilities, and implementing effective solutions.”

Adnan Hadžiahmetović Cyber Security Engineer, Personify Health · CCSP Same team · February 2024

“Elvir possesses an outstanding proficiency in Network Security Implementation, Infrastructure Security, Endpoint Security, and Security Incident & Event Management. His expertise in these domains is truly commendable and has significantly contributed to the overall security posture of our organization.”

Mersad Huskic AI Architect & Senior Tech Lead · CISSP Colleague, different team · February 2024
All recommendations on LinkedIn →
Experience

Where I've worked.

Jul 2024 – present Full-time

Software Engineer – IAM

Personify Health d.o.o. (formerly Virgin Pulse)

Operate the multi-realm Keycloak platform that acts as the central identity broker for the company's products and internal services: hundreds of external SAML 2.0 and OIDC federations, Okta, PingIdentity, Microsoft Entra ID, LDAP / AD federation, protocol mappers for custom JWT claims, SSO configuration in Terraform, Python automation, and an AI agent on AWS Bedrock that turns SSO tickets into reviewed configuration changes.

Apr 2026 – Jun 2026 Contract

Senior Backend Engineer – IAM

UK proptech · B2B contract via Explore Group

Sole Keycloak technical owner on a fixed-term engagement: greenfield partner-authentication realm, Keycloak configuration as code with Terragrunt, and the pre-go-live security review.

Aug 2022 – Jul 2024 Full-time

Cyber Security Analyst

Virgin Pulse d.o.o.

Administered Microsoft Entra ID — conditional access, MFA enforcement, identity governance and access reviews across Microsoft 365 and Azure. Developed IAM security policies for Azure and built Python + Rapid7 automation for account lockdown.

Dec 2021 – Aug 2022 Full-time

System Analyst

Virgin Pulse d.o.o.

Managed Active Directory accounts, groups and access provisioning across the identity lifecycle — onboarding, offboarding and recertification.

Education — Master’s (2021–2026) and bachelor’s (2016–2020) degrees in Communication Technologies, University of Sarajevo. Master's thesis: continuous integration and delivery of software in cloud environments.

Also building · in development

Aldera

Privacy-compliance software for companies in Bosnia and Herzegovina, mapped article by article to the new Law on Personal Data Protection (Sl. glasnik BiH 12/25). I'm building it myself: a multi-tenant Django application on PostgreSQL, with row-level security enforcing tenant isolation in the database.

Contact

Working on identity? Let's talk.

Send a short email — what you run today, what is hurting and any deadline. I'll reply with a time for a free 30-minute call.